Ambiguous incidents
Malware, intrusion, and insider cases where the first job is establishing what the evidence supports.
About
Investigation, product building, doctoral research, and production security engineering connect through one habit: establish what the evidence supports, then decide what to do next.
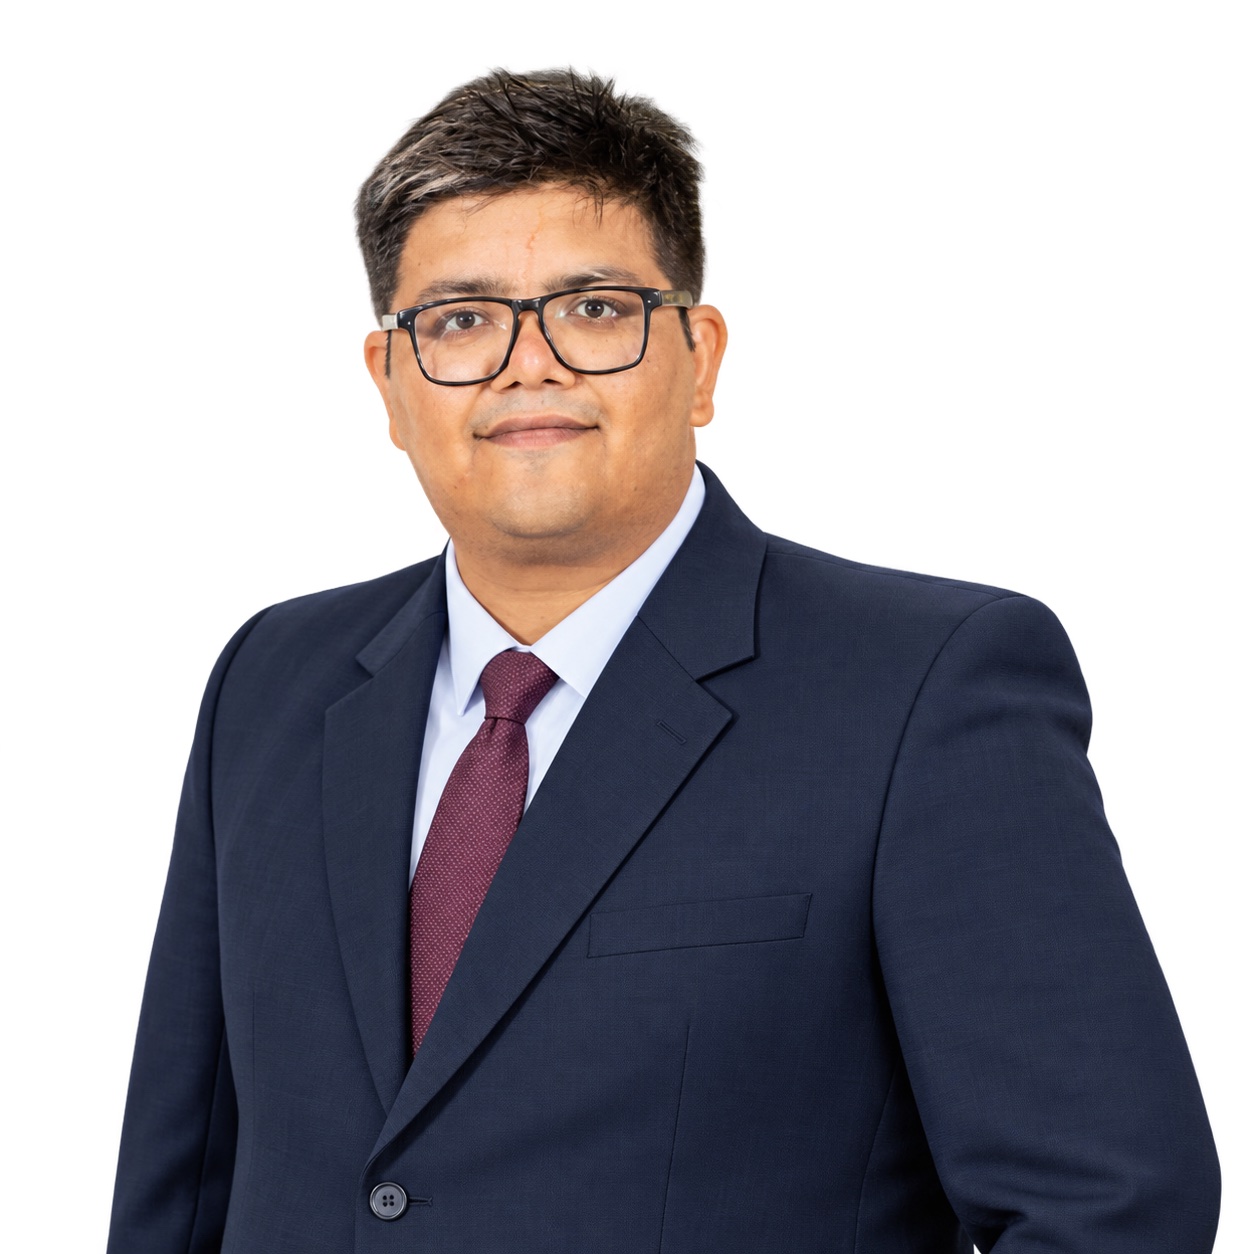
I combine more than fifteen years of cybersecurity work with security engineering and applied research. I investigate malware and intrusions, review architectures and access paths, protect sensitive data, and share what I learn through teaching, writing, and speaking.
The path has moved through classrooms in Gujarat, early consulting and product companies, doctoral work on insider threats, and large-scale engineering. Earlier malware-response and consulting engagements are separate from my current employment responsibilities, which I describe only at a public level.

Career
A path from investigation and teaching to products, research, and security engineering.
2010
I founded Pratikar Technologies in 2010 and began hands-on consulting and investigation work. An October 2009 “Introducing Pratikar” note was an early announcement before that founding year.

2011–2012
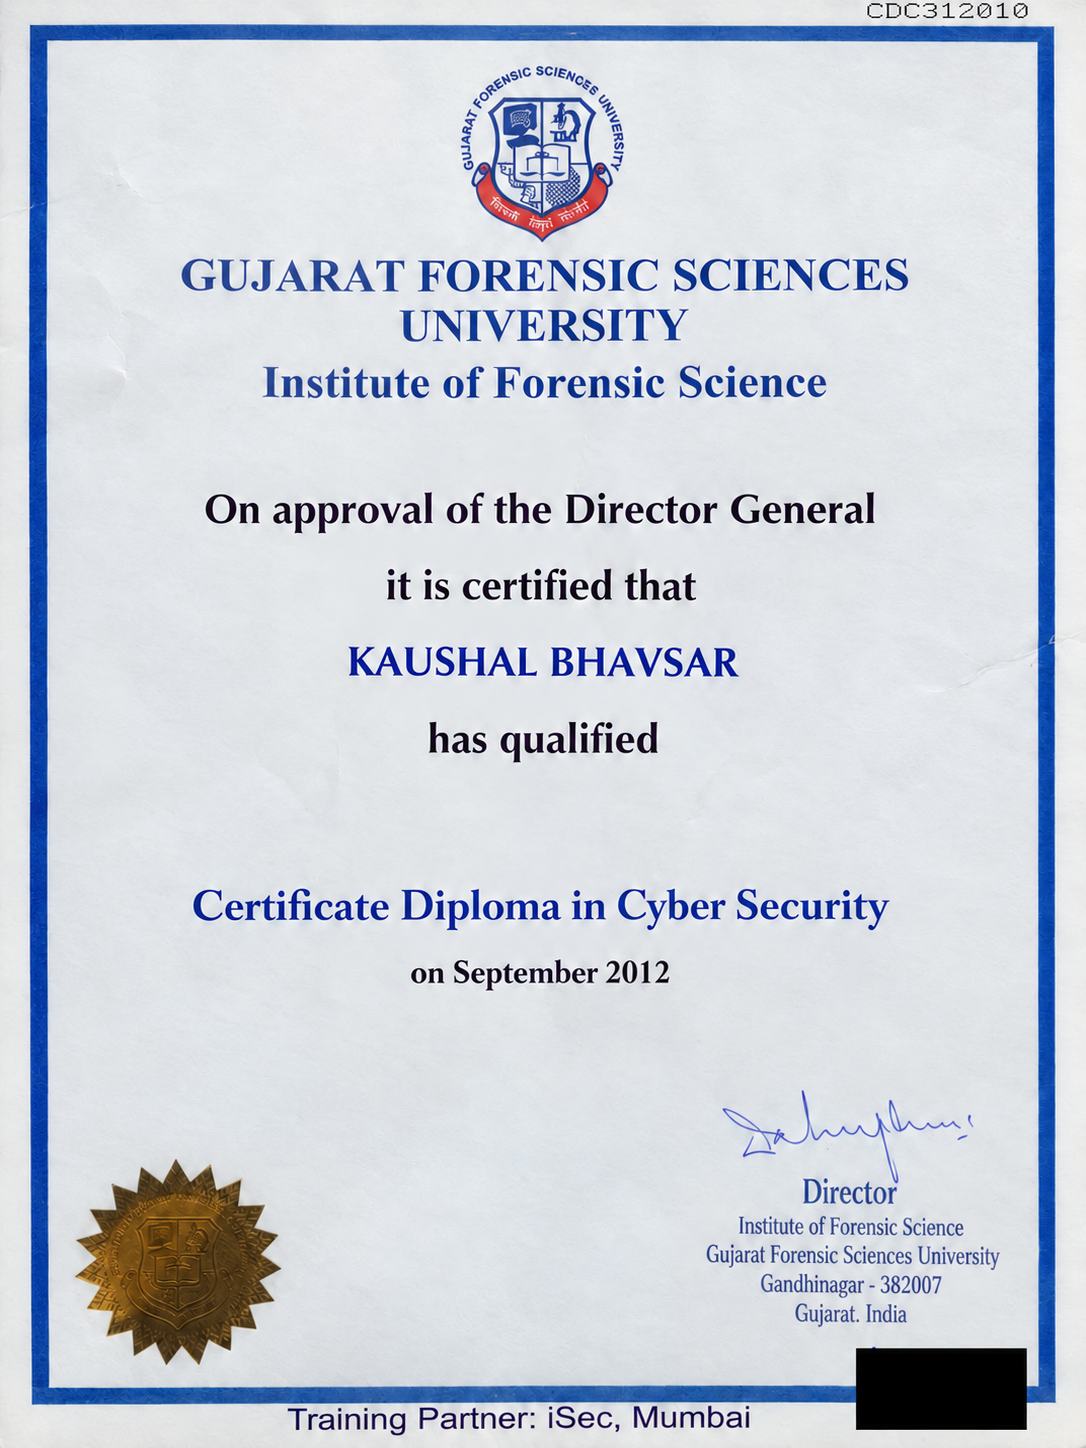
I was part of GFSU’s inaugural Certificate Diploma in Cyber Security batch and passed in 2011. The certificate was awarded in 2012. That foundation sharpened how I think about evidence, investigation, and disciplined analysis.
Teaching
I taught Network Security at Gujarat University and designed syllabi for Network Security, Web Security, and Information Security courses for postgraduate students. I also developed a Networking & Security Research Lab at Rollwala Computer Center.

2012
In January 2012 I left academia for full-time entrepreneurship and co-founded Anatag and Bizmica — SaaS products that pushed me from explaining security problems to shipping software people rely on. Anatag later participated in Microsoft Appfest.

2015
In December 2015 I founded BUGSKAN and built a cloud vulnerability scanner, later adding cloud WAF capability under the BugShield Security-as-a-Service platform. BugShield and the original BUGSKAN scanner are discontinued; they remain part of my product history.

2019
I joined GoDaddy in April 2019. My public title is SDE – Data Privacy and Security. I work on larger-scale security and data-protection challenges in production environments.

2021–2022
I submitted my PhD thesis, Prediction of Insider Cyber Threats Using Behavioral Analysis, at GLS University in 2021 after synopsis and defense milestones recorded on satark.org. The degree was conferred in March 2022. The work sits in the SATARK research line on behavioral prediction, Threat-Rank scoring, and related forensic studies.

Today
I continue engineering work in data privacy and security while writing, speaking, and taking scoped consulting and research collaborations. I keep employer-confidential systems, data classes, and internal metrics out of public materials.

Focus
I am drawn to problems where investigation, engineering, and clear communication all matter.
Malware, intrusion, and insider cases where the first job is establishing what the evidence supports.
Architecture and engineering choices that hold up across real production systems and noisy data.
Using research and machine learning carefully — especially for novel malware and behavioral risk.
Teaching, mentoring, and writing that help others apply security practice without empty jargon.
Research
My doctoral thesis at GLS University — Prediction of Insider Cyber Threats Using Behavioral Analysis — is part of the SATARK research lineage (satark.org). I am also the named inventor on US12361127B1, “Computer-based systems configured for malware detection and methods of use thereof,” granted in July 2025. Inventorship does not mean personal ownership of the patent.

Building
Building Anatag, Bizmica, BUGSKAN, and BugShield taught me the distance between a security idea and a product customers can operate. BUGSKAN’s original scanner and BugShield are discontinued; they remain documented historical work, not active products.
Community
I have designed postgraduate security curricula, built a research lab, spoken with media about practical cyber risk, and written for practitioners. Sharing knowledge is how good security practice spreads.

Philosophy
Investigate threats. Engineer security. Share knowledge.
I start by establishing what the evidence supports. I then explain the risks, identify what remains uncertain, and recommend practical next steps.
I prefer work where investigation, engineering, and clear writing all matter — consulting, product building, or research collaboration.